
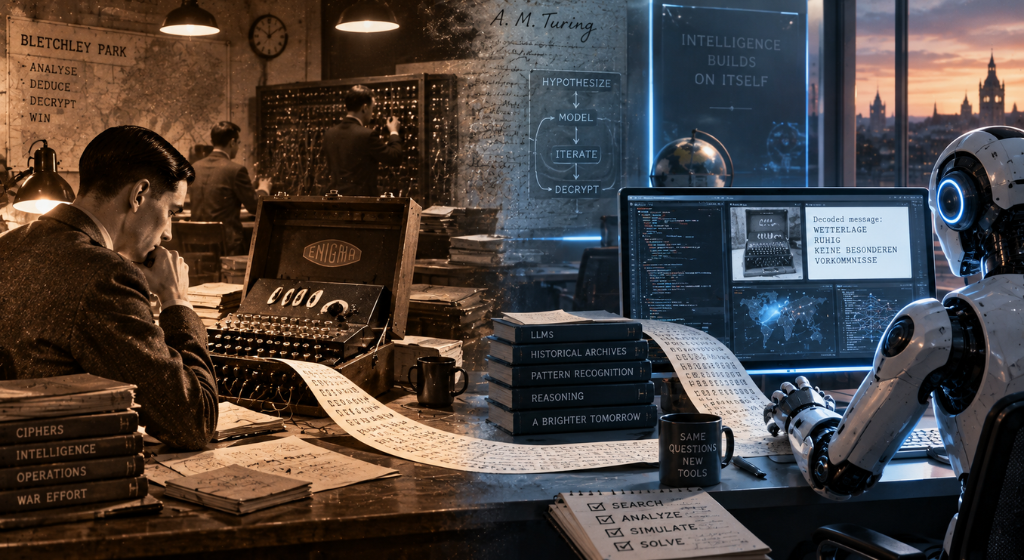
AI is rapidly increasing the number of software vulnerabilities researchers can uncover, creating a growing gap between automated bug discovery and the human teams responsible for fixing and deploying patches. (Source: Image by RR)
Microsoft, Oracle and Google Report Surging Numbers of Security Fixes
Artificial intelligence is dramatically accelerating the discovery of software vulnerabilities, creating a new cybersecurity challenge even as leading AI companies debate slowing development of more powerful frontier models. Widely available AI systems are already helping researchers uncover security flaws at unprecedented scale, increasing pressure on developers, corporate security teams and open-source maintainers responsible for fixing them. The shift means one major consequence of increasingly capable AI has already arrived: vulnerability discovery is beginning to scale with computing power while remediation remains constrained by human time and expertise.
The numbers illustrate how quickly the landscape is changing. Microsoft, as noted in an article at wired.com, said it issued patches for 974 vulnerabilities this month, while Oracle released 1,448 patches in July compared with 309 during the same month last year. Two major Google Chrome releases in June included 1,072 fixes—more than the previous 23 major releases combined—and Mozilla reported finding 271 Firefox vulnerabilities during a single AI-assisted bug-hunting sprint using Anthropic’s Mythos model. Across the industry, 66,401 common vulnerabilities and exposures had been recorded as of September 16, nearly double the 33,512 recorded by the same point last year and far above the roughly 25,000 reported during all of 2022.
More discovered vulnerabilities do not automatically mean software is becoming less secure. Finding and disclosing previously unknown flaws gives developers an opportunity to repair weaknesses before attackers exploit them, and AI is increasingly helping defenders perform that work. The concern is that discovery may begin moving faster than remediation. Developers must still understand vulnerabilities, create patches, test fixes, distribute updates and convince organizations and users to install them—all processes that remain heavily dependent on people. Attackers meanwhile have access to many of the same AI capabilities, potentially allowing them to search for previously unknown weaknesses at increasing scale.
For now, researchers describe an uneasy balance in which AI is empowering both attackers and defenders. A slowdown in development of future frontier models could potentially reduce some emerging risks, but it would not eliminate the cybersecurity pressures created by AI systems already widely available today. The emerging bottleneck is therefore shifting away from the ability to discover security flaws and toward the capacity to repair them quickly enough, creating a cybersecurity race between increasingly automated discovery and fundamentally human remediation.
read more at wired.com





Leave A Comment